DKE 365 on DuoKey Cockpit v2
The DuoKey Cockpit for DKE 365 — its configuration surface, key lifecycle and access policies.
Sequence
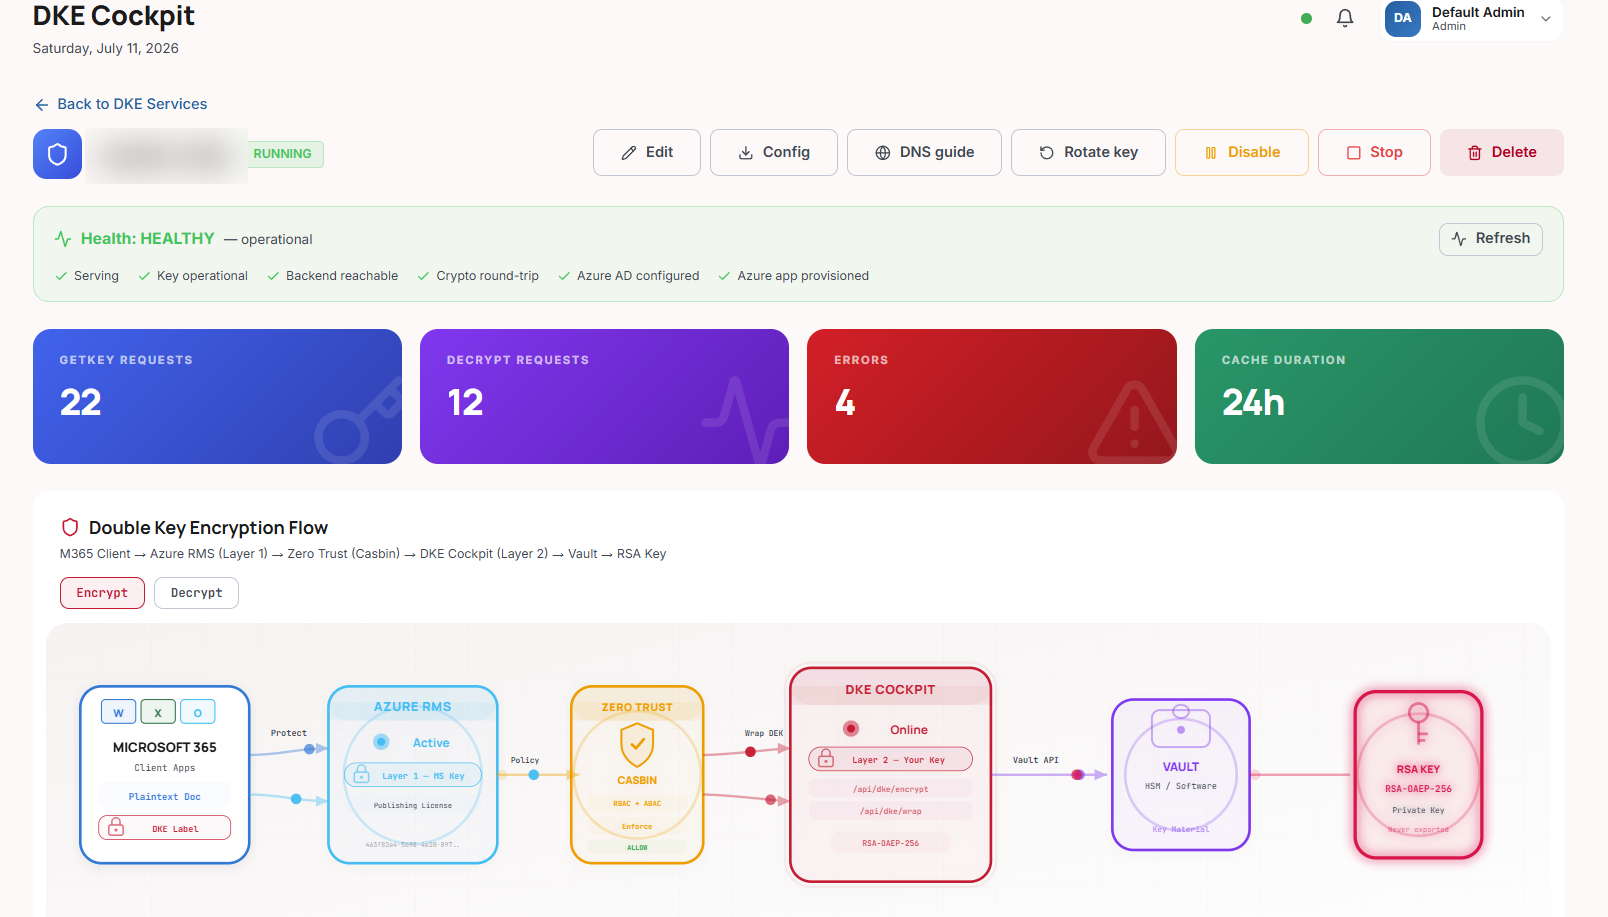
A DKE decrypt on Cockpit v2
Office calls the DKE service with its Entra ID token. The policy engine decides, the decision is recorded in the audit trail, and only an allowed call reaches the vault-held RSA key. See Access Policies.
Some pages in the wider DKE guide still show screenshots of an older console. The behaviour documented in this section reflects the current Cockpit; refreshed screenshots are being rolled out progressively.
What changed for DKE 365 in Cockpit v2
DKE (Double Key Encryption) protects Microsoft 365 / Purview content with two keys: one held by Microsoft (Azure) and one held by your organization. Cockpit v2 hosts the organization-side RSA key and serves the Microsoft-compatible GetKey and Decrypt operations — now with a redesigned configuration model.
Highlights of the v2 DKE implementation:
Clean management surface
A streamlined management surface to deploy, enable, rotate and monitor DKE services, plus the public protocol endpoints that Office calls directly.
Rotation without relabelling
Stable label URL and key history — a rotation does not change the URL in the sensitivity label, and rotated-out keys stay decrypt-only until an administrator retires them, so existing content stays readable.
Azure AD provisioning
Automatic Azure AD app provisioning via Microsoft Graph on enable.
B2B partner domains
B2B partner-domain support (each allowed domain maps to its own tenant's valid token issuers).
Access-policy engine
A policy engine (RBAC + ABAC) for access control (user / IP / location / time / group) — see Access Policies.
Platform (recap)
Cockpit v2 is the next-generation rewrite of the DuoKey platform. Security highlights that apply to DKE: strong authentication (JWT + WebAuthn), a policy engine (RBAC + ABAC) for authorization, AES-256-GCM encryption at rest, and a tamper-evident, hash-chained audit trail with fail-closed guarantees for security-relevant events. Cockpit v2 is multi-tenant, with each tenant's data isolated automatically.
Keys are held in the tenant vault — DuoKey KMS (software MPC by default) plus HSM backends including Securosys (FIPS 140-2 Level 3 & 4). The DKE private key never leaves the vault.
The same Cockpit v2 platform powers every DuoKey integration. For a broader platform overview, see Oracle TDE → Overview — the platform description there applies to DKE 365 as well.
DKE 365 on the Cockpit — at a glance
| Dimension | DuoKey Cockpit |
|---|---|
| Key algorithm | RSA-OAEP-256 (default) or RS256 |
| Key rotation | Stable label URL; rotated-out keys stay decrypt-only until retired |
| Decrypt auth | Azure AD JWT + optional mTLS (reverse-proxy) + access-policy enforcement |
| Access control | Policy engine — RBAC + ABAC (user / IP / location / time / group) |
Any throughput, latency or footprint figures quoted for Cockpit v2 are vendor targets, not independently benchmarked guarantees.
What's in this section
DKE Configuration
The DKE service configuration functions in Cockpit v2 (deploy, enable, rotate, GetKey/Decrypt, Azure AD provisioning, host settings, Purview).
Access Policies
The RBAC + ABAC model and how policies protect DKE services.
Key Rotation
Rotate the service key by hand or on a schedule (30, 180, 365 days or custom), with quorum approval and failure alerts.